The Cloudflare alternative from Germany
CDN64 makes your website or service reachable via the IPv64.net edge servers in Germany – over IPv4 and IPv6, even behind DS-Lite and CGNAT. With Node64 it runs through a tunnel from your home network, with no open port and end-to-end encrypted if you like.
4 edge servers in Nuremberg & Falkenstein IPv4 & IPv6 HTTP/3 DS-Lite & CGNAT Made in Germany
Create a free account The three modes Documentation Server statusWhat Cloudflare Tunnel and proxy do – operated in Germany, with your ipv64.net account and your ipv64 domains.
Node64 opens the tunnel from your home network to the outside. Every port on your router stays closed and your own IP address stays hidden – even behind DS-Lite and CGNAT, via IPv4 and IPv6.
In the default mode the edge servers only pass the connection through: TLS ends at your place, certificate and key stay on your node. The servers never see contents, paths or cookies.
Four edge servers in Nuremberg and Falkenstein, operated by IPv64.net. No detour via data centres overseas.
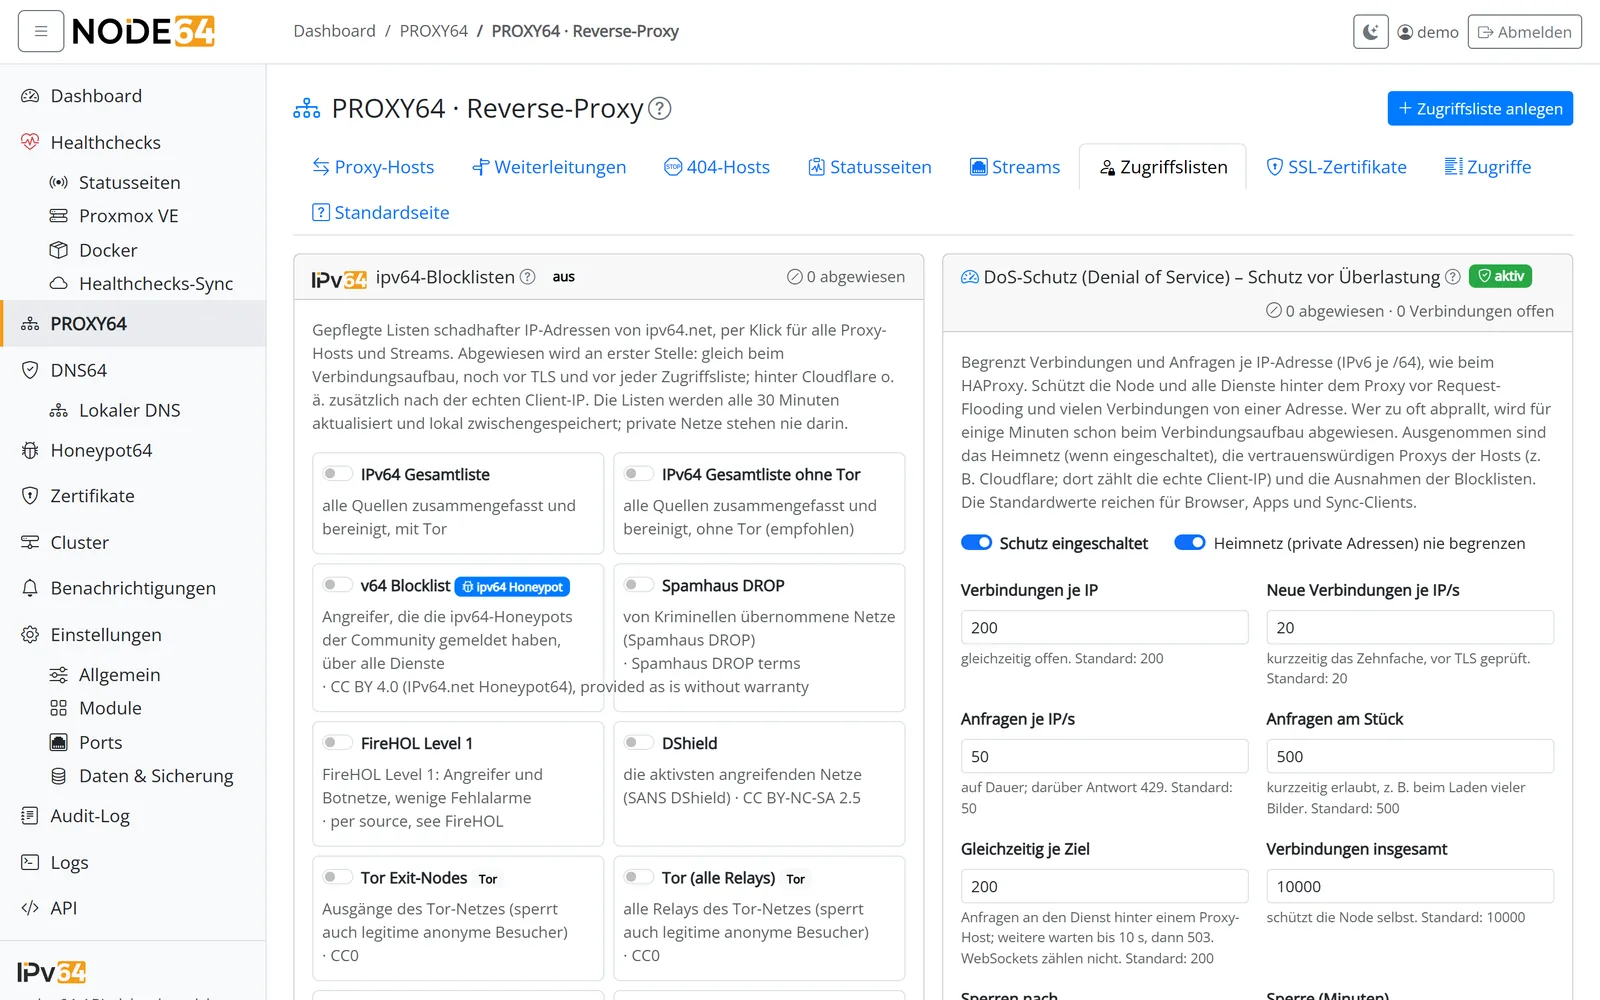
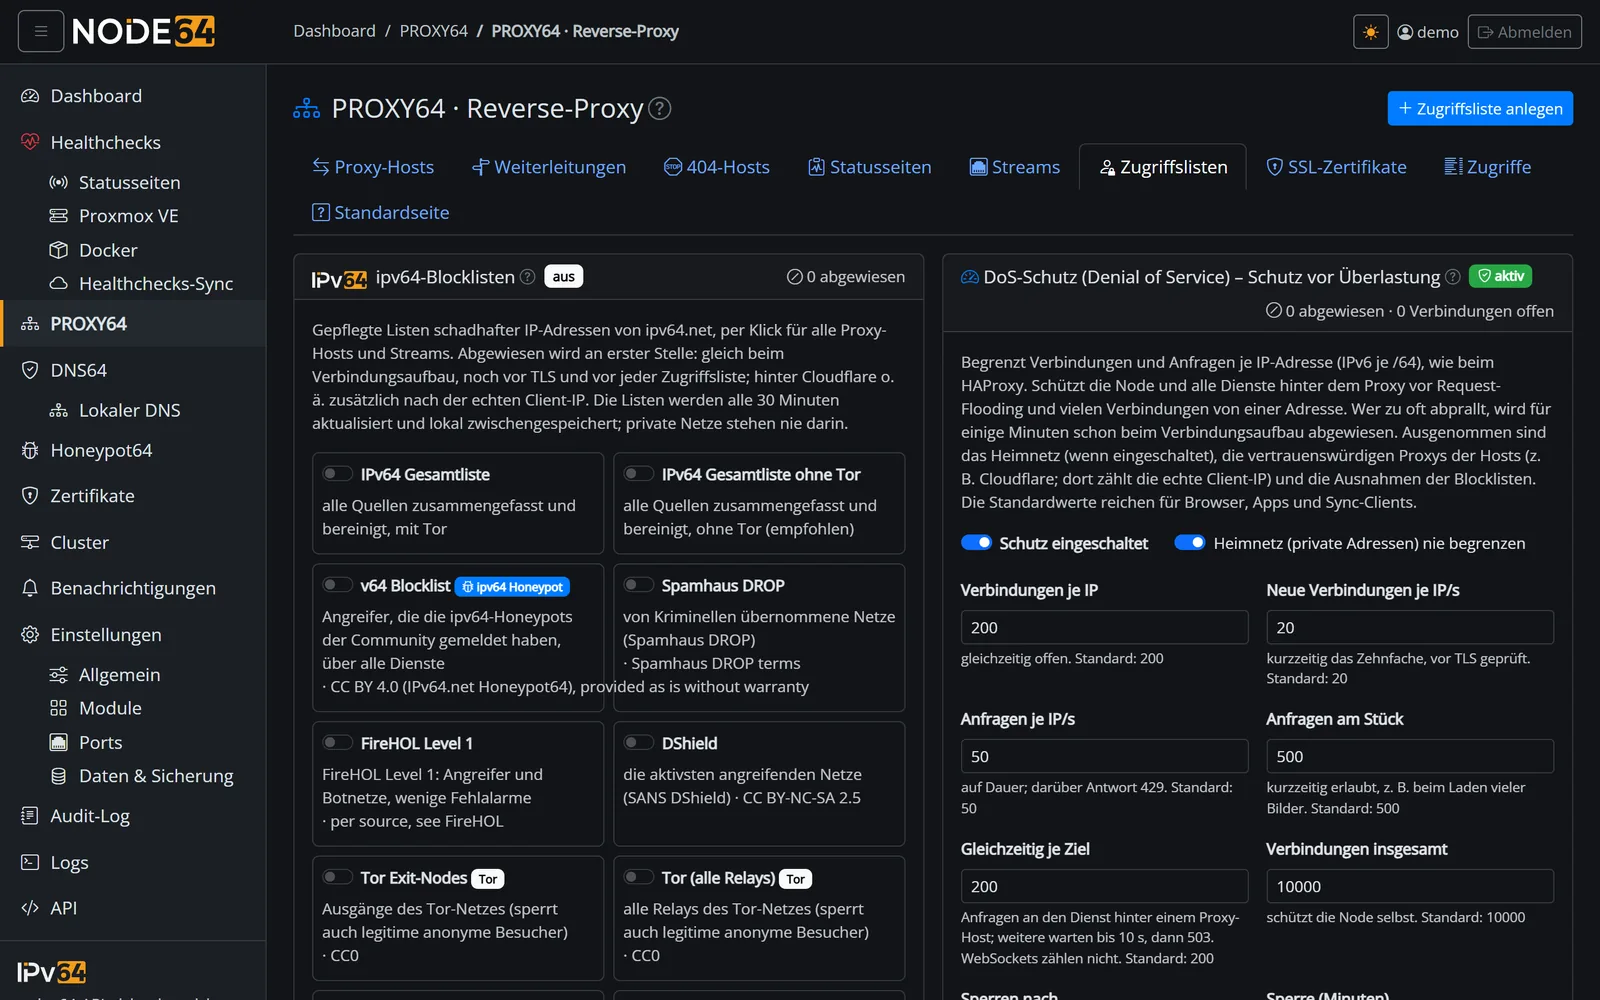
Access lists, a pause button for attacks, limits per IP, WAF patterns and detection of attack tools already act on the edge servers – before an attacker reaches your connection.
Several servers via DNS, an automatic replacement server if one fails and load balancing that moves without interruption.
Not just websites: with the port mapper you also reach TCP and UDP services such as game servers or SSH via the edge servers.
The mode decides where encryption (TLS) ends and how the edge servers reach your service. You can switch between modes 1 and 2 at any time; DNS stays the same.
Default, with Node64
The edge servers only read the name from the connection setup and pass the connection through the tunnel to Node64 unencrypted by them. TLS ends on your node, your certificate stays with you. HTTP/3 is passed through as well. The right choice for almost everything.
with Node64
The edge servers terminate TLS themselves (HTTP/1.1, HTTP/2, HTTP/3) and send every request with the real visitor IP through the tunnel. That way they filter before your connection: limits per IP, host check, redirect to HTTPS. The servers fetch the certificate themselves.
without Node64, on ipv64.net
No tunnel: the edge servers connect directly to your publicly reachable target – like a classic reverse proxy in front of your server. The target is your domain's A/AAAA records or a fixed address. Plus an optional cache on the servers.
| Mode 1 – pass-through | Mode 2 – TLS on the servers | Mode 3 – straight to the target | |
|---|---|---|---|
| Path to the service | Node64 tunnel | Node64 tunnel | direct, no tunnel |
| TLS ends | on your node | on the edge servers | on the edge servers |
| Open port at home | no | no | yes |
| Own IP hidden | yes | yes | no |
| Cache on the servers | no | no | yes, optional |
| Set up in | Node64 | Node64 | ipv64.net/cdn64 or API |

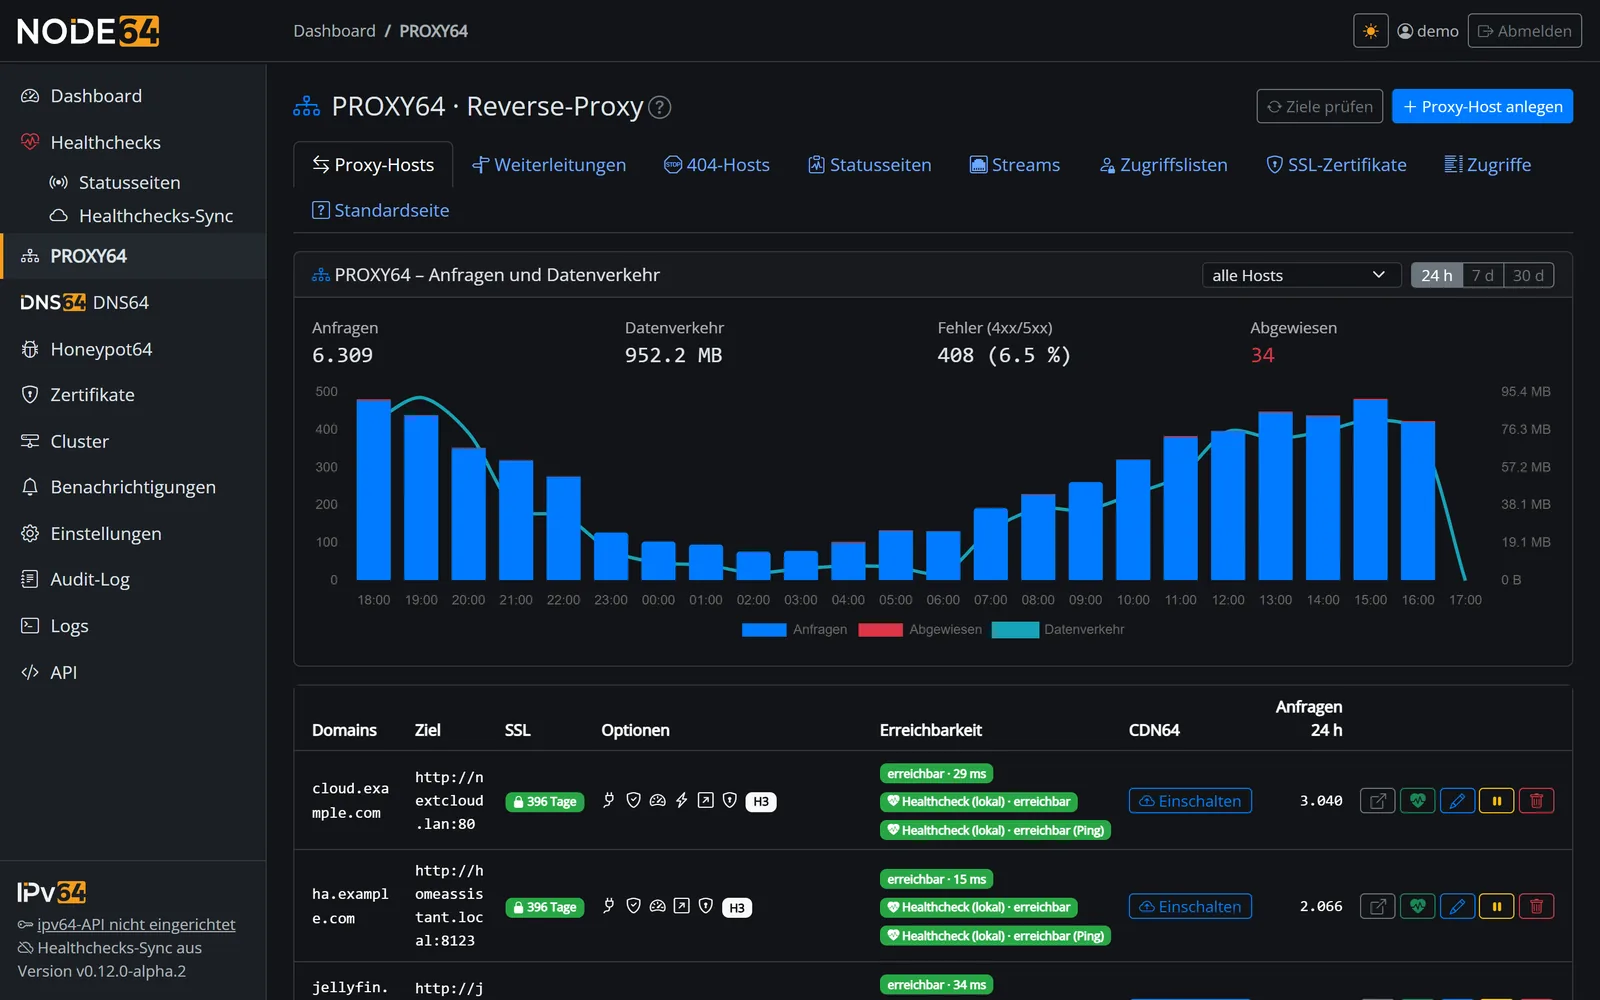
In Node64 you switch on CDN64 per proxy host with one click. Node64 fetches Let's Encrypt certificates, opens the tunnel and shows which servers it currently runs through. More about Node64

The ipv64 blocklists – including the v64 Blocklist from the community honeypots – and DoS protection with limits per IP are switched on in PROXY64 with one click.
The account class decides how many edge servers a name runs through.
Already have an account? Log in at the top – then you manage your CDN64 names here.